Appearance
Creating and Managing API Tokens in Easy MCP AI
Easy MCP AI uses API tokens to authenticate AI clients that connect to your WordPress site with a manual configuration. Each token is tied to a WordPress user, can be limited to specific tools, and can be set to expire. You stay in control of exactly what a connected AI is allowed to do.
In this article
When You Need a Token
You only need an API token for clients you connect manually, by pasting a configuration file or an Authorization header.
Clients that support OAuth (such as Claude.ai, Claude Desktop, Cursor, or ChatGPT) don't need a token at all: you point them at your MCP endpoint URL, log in to WordPress once, and the plugin manages credentials automatically.
If you haven't installed the plugin yet, start with the Getting Started guide.
How to Create a Token
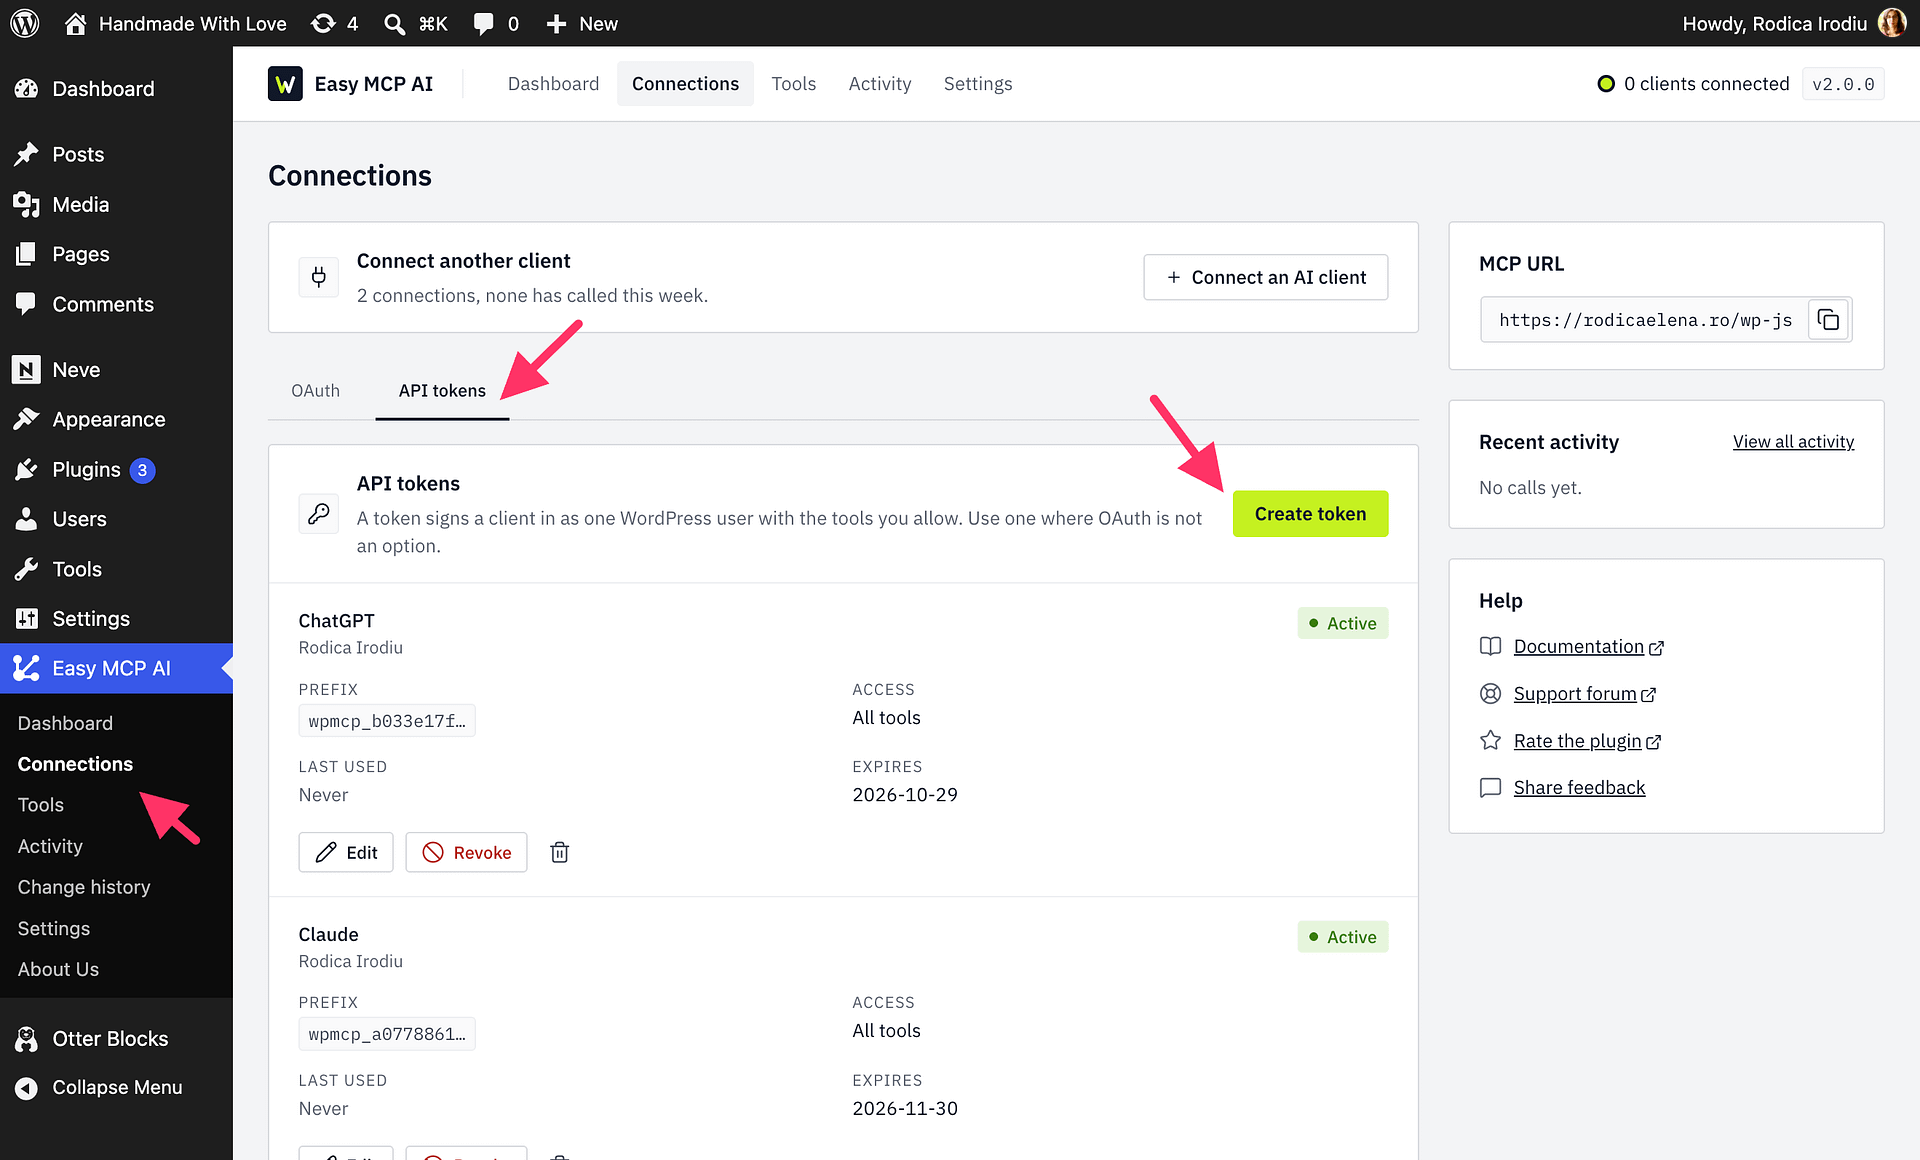
- In your WordPress dashboard, go to Easy MCP AI > Connections > API tokens.
- Click Create token.
- Fill in the token details and click Create token.
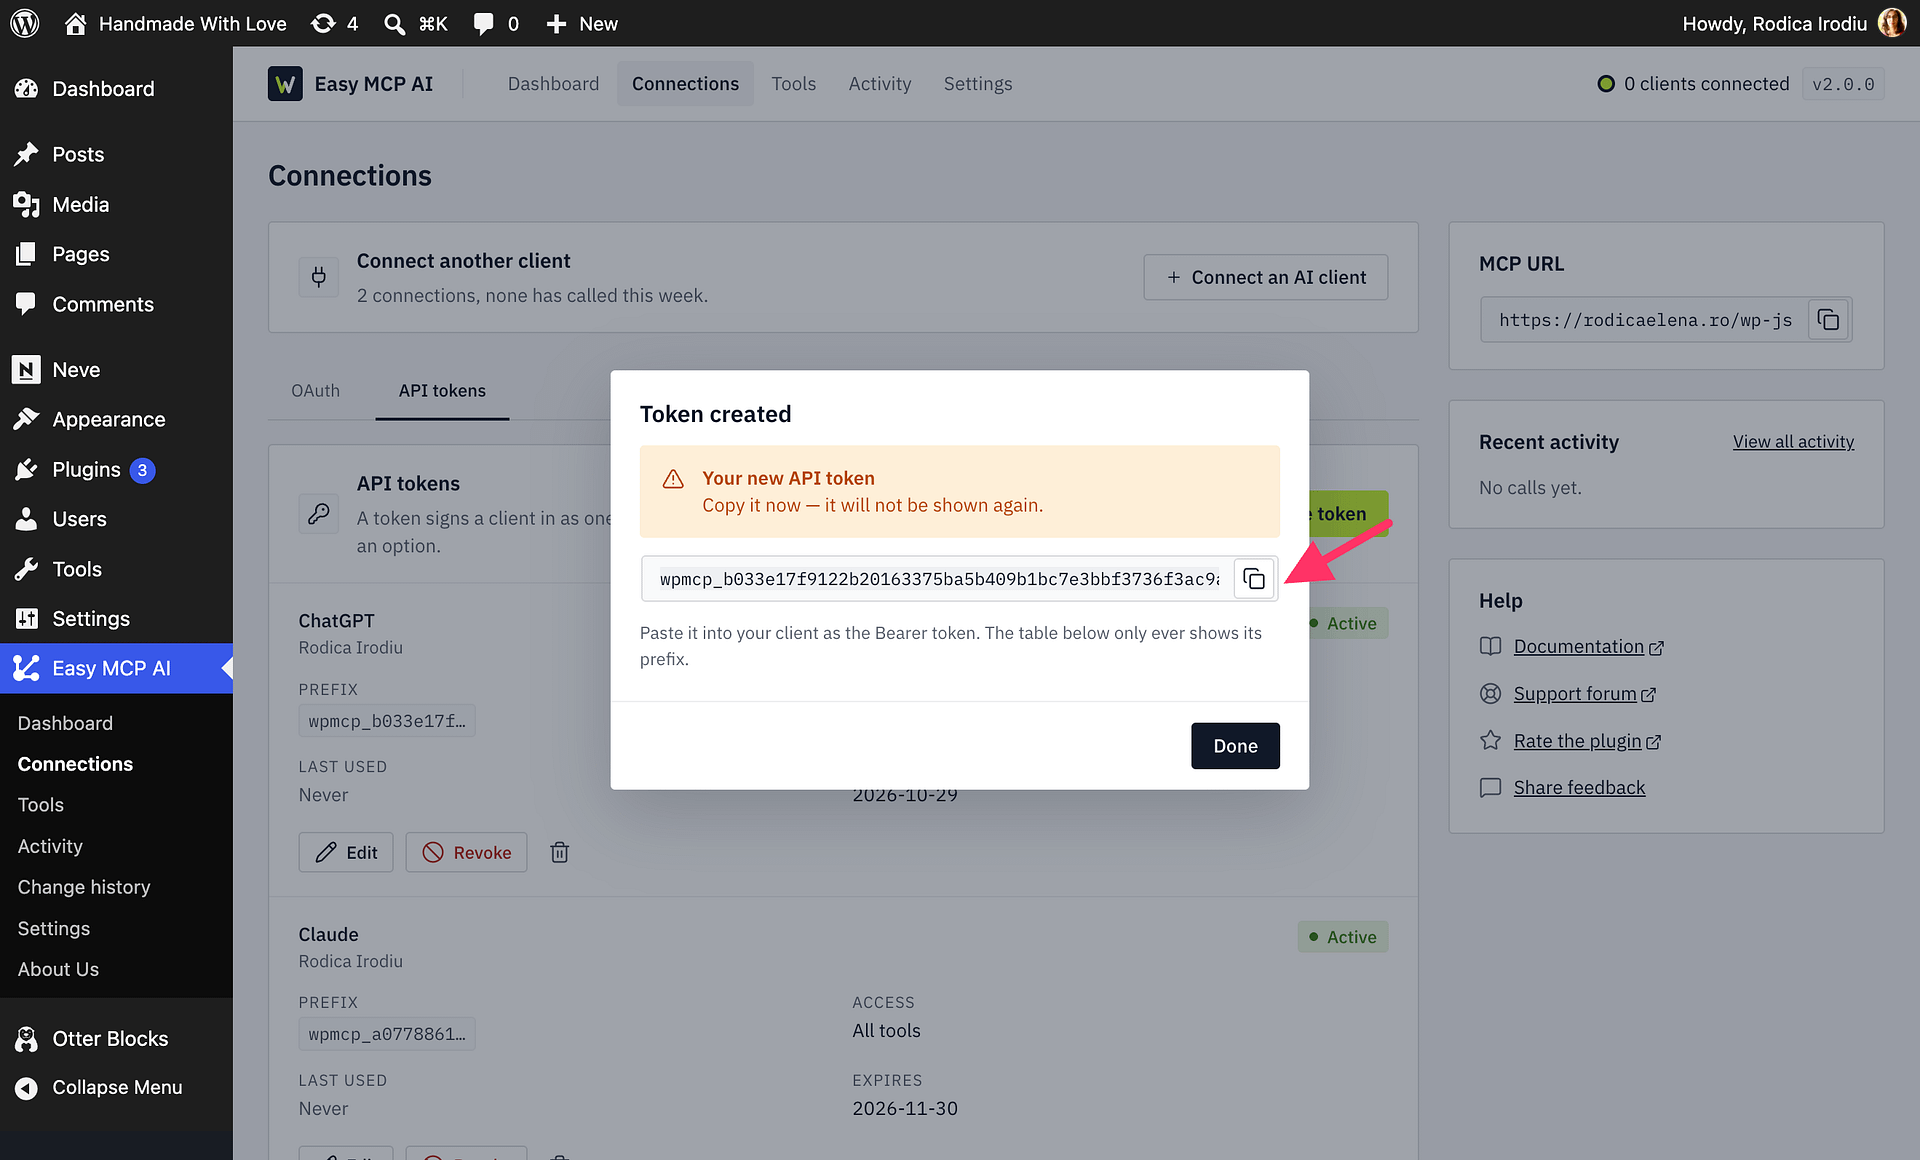
Your new token is displayed only once, right after creation. It looks like wpmcp_a1b2c3…. Copy it immediately and store it somewhere safe. Only its SHA-256 hash is saved in the database, so it can never be shown again. If you lose it, revoke it and create a new one.
Token Name
A descriptive name that identifies where the token is used, for example "Claude Code - Production". Naming tokens after the client and site makes it easy to spot which one to revoke later.
WordPress User
The token acts as this user: every tool call is checked against the user's WordPress permissions. Tokens can only be assigned to Administrators, Editors, or Authors.
- Administrator: full access, including plugins, themes, users, and site settings (where those tools are enabled).
- Editor: content-only access, covering posts, pages, media, comments, and taxonomies.
- Author: the most restricted option, limited to publishing and managing their own posts.
Choose the least powerful user that can still do the job. For a content-writing assistant, an Editor is usually the right choice.
Expiration Date
New tokens default to 30 days. You can instead choose 7 days, 60 days, or 90 days; each preset shows the exact expiration date it will use. Choose Custom to pick another future date, or No expiration for a token that does not expire. Expired tokens stop authenticating automatically, and you can change the expiration later by editing the token.
Tool Permissions
Choose an Access level when creating or editing a token:
- Read-only allows tools that inspect the site without changing it.
- Full access allows all current and future tools permitted to the selected WordPress user. This includes any privileged tool switched on for the site, and the dialog shows a warning naming them while one is on.
- Custom opens the per-tool picker so you can grant only the required categories and actions.
Granting write or delete permissions allows the AI to create, modify, or permanently remove content on your site. Review every non-read-only permission before granting it, and only select tools you actually use.
Using a Token
Pass the token as a Bearer header when configuring your AI client:
Authorization: Bearer YOUR_API_TOKENagainst your site's MCP endpoint:
https://yoursite.com/wp-json/easy-mcp-ai/v1/mcpFor clients that cannot send custom headers, the token can be appended to the endpoint URL instead (…/v1/mcp/YOUR_API_TOKEN). Treat this as a last resort: URL-based tokens appear in server access logs, WordPress debug logs, and browser history. Use the Authorization header whenever possible.
Managing Existing Tokens
The API Token tab lists all your tokens with their name, token prefix, user, allowed tools, last-used time, expiration, and status. Only the prefix is shown; the full token cannot be retrieved after creation.
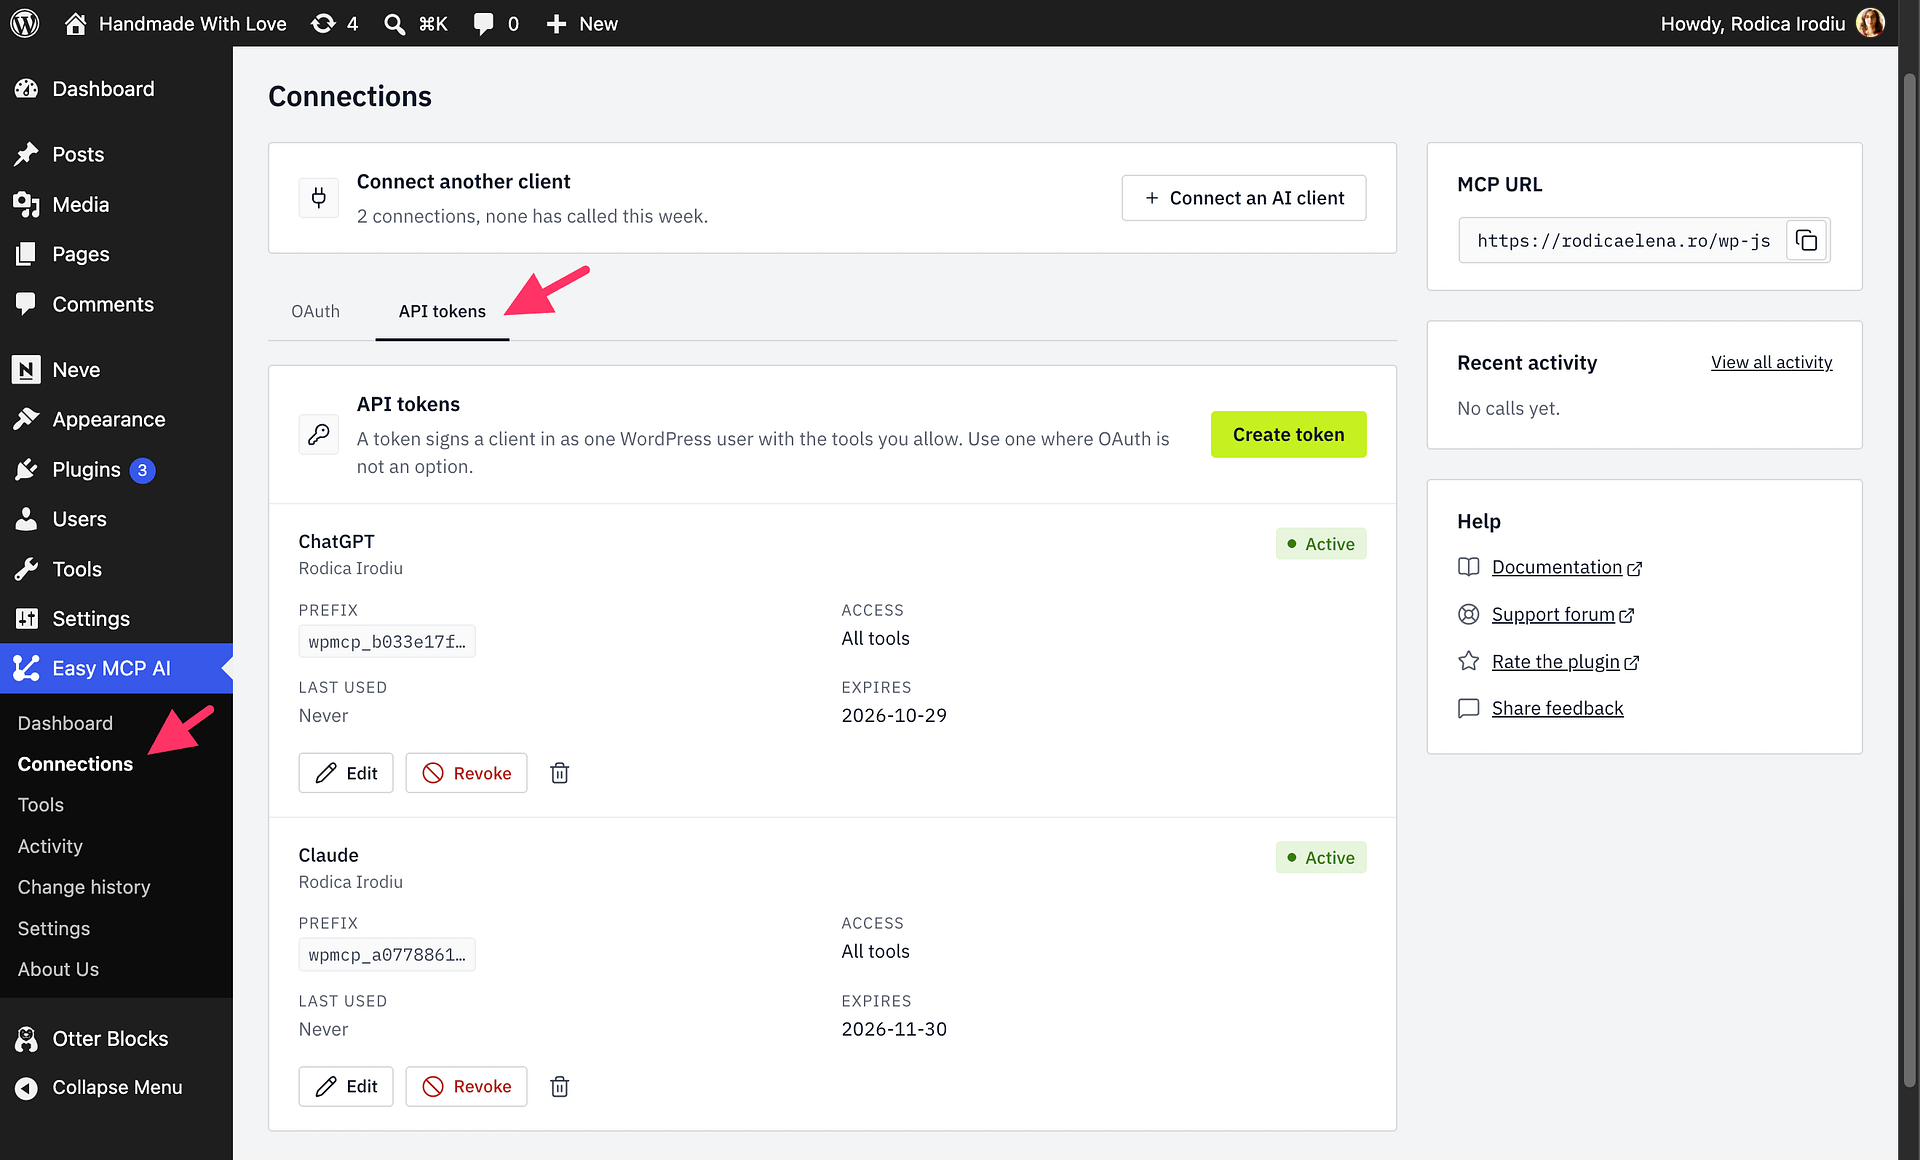
For each token you can:
- Edit: rename it, reassign the user, change the expiration date, adjust tool permissions, or temporarily deactivate it with the Active checkbox.
- Revoke: permanently stop the token from authenticating while keeping its record in the list.
- Delete: remove the token entirely. This cannot be undone.
If a client stops working after a token change, create a fresh token and update the client's configuration. The old value can't be recovered.
Self-Service API Keys
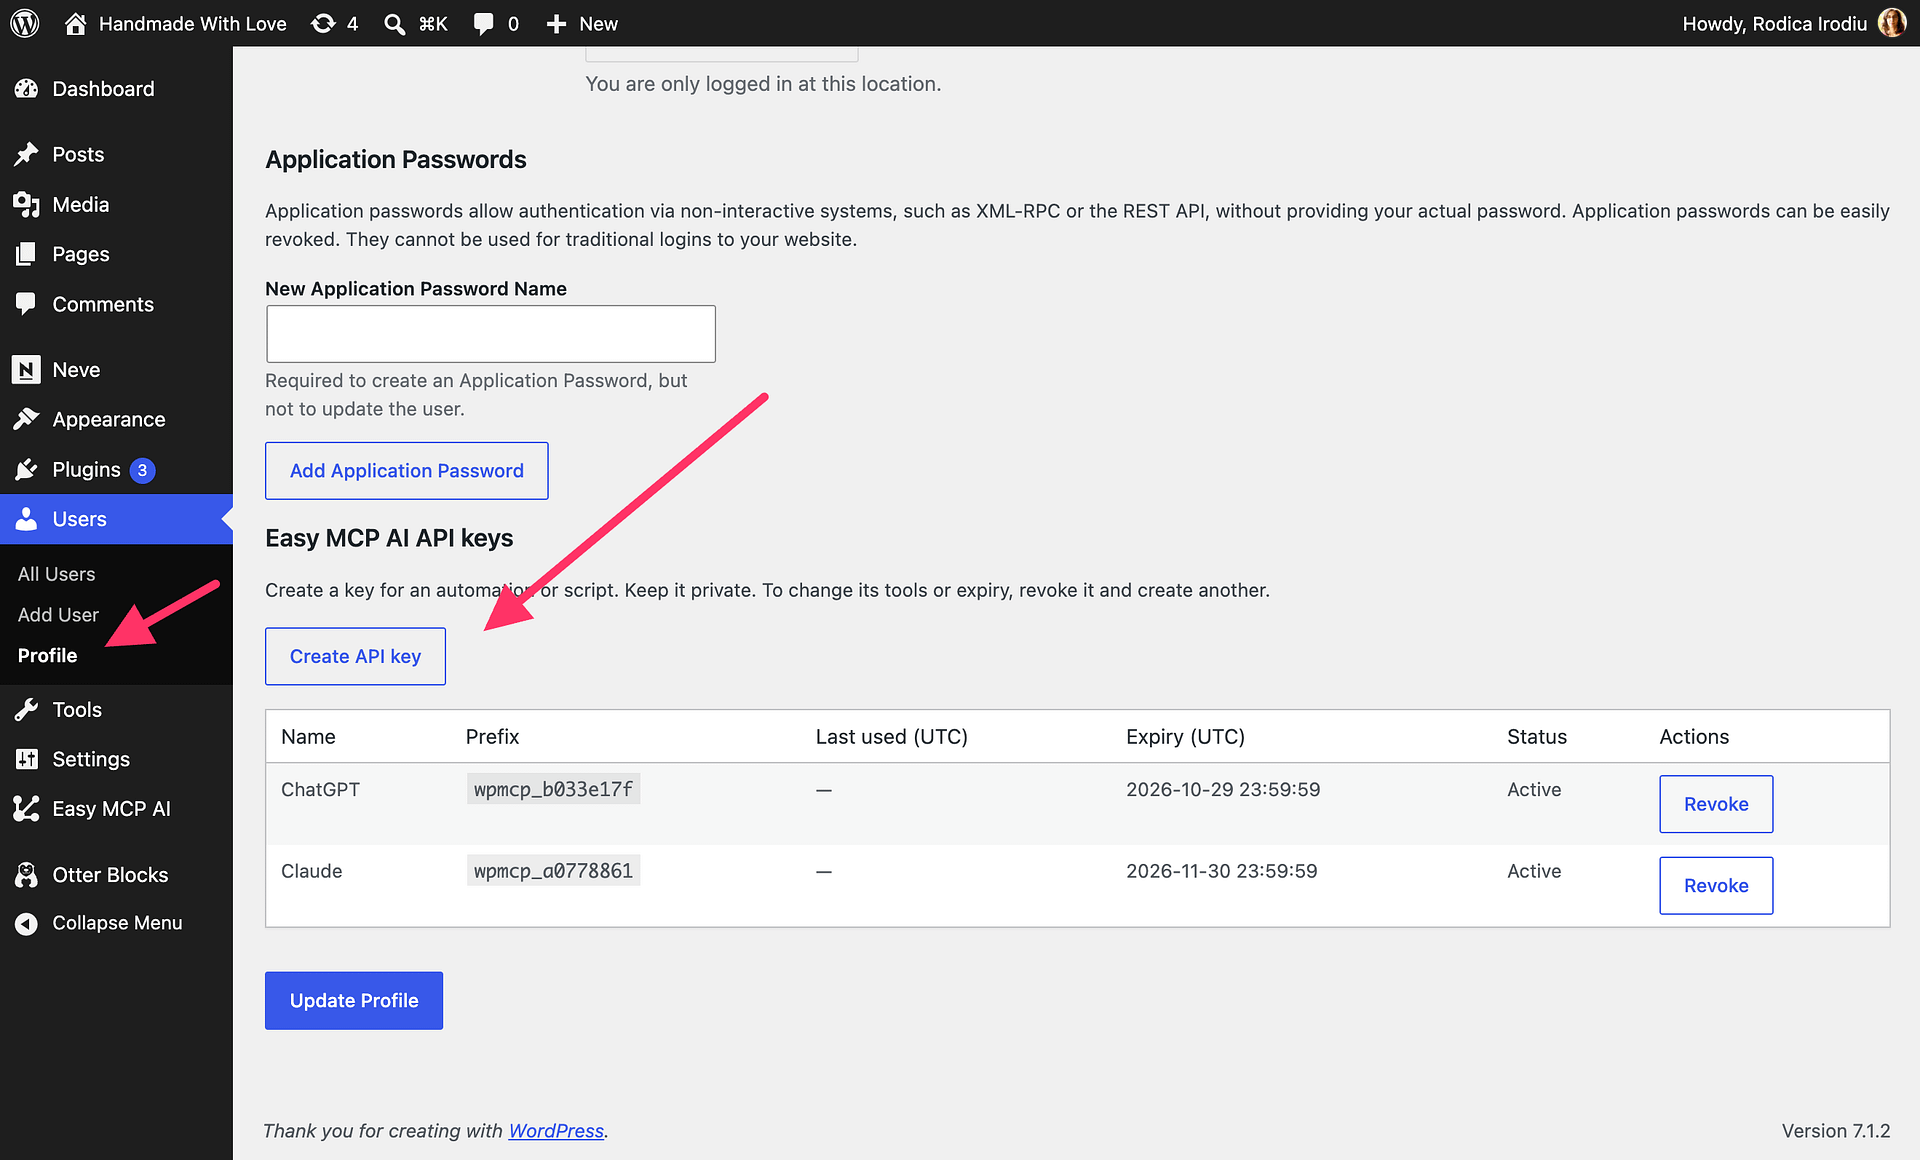
By default, only administrators can create tokens, and only from the API tokens tab. When an administrator turns on Self-service API keys in Easy MCP AI > Settings, eligible users can also create and manage their own keys without administrator help.
- Eligibility: the administrator chooses which WordPress roles are allowed to self-serve when enabling the feature. Only users with one of those roles see the self-service option.
- Where to find it: eligible users go to their own WordPress profile page (Users > Profile, or Your Profile in the admin toolbar) and use the API keys section there to create a key for themselves.
- Creation limit: the administrator sets a maximum number of active keys per user. Once a user reaches that limit, they must revoke one of their existing keys before creating another.
- One-time secret: as with administrator-created tokens, the full key is shown only once, right after creation. Copy it immediately — only its hash is stored, so it can never be displayed again.
- Owner-only revocation: users can revoke only the keys they created for themselves. They cannot view, edit, or revoke another user's keys, and self-service keys still count toward, and are still subject to, every tool permission and site-wide guardrail described below.
Keys After a Clone or Domain Move
API keys are bound to the site that issued them, not just to the user or the token value itself.
- Cloned or copied sites: if you copy the site's database to a different hostname, for example to spin up a staging copy or migrate to a new host, keys issued on the original site do not work on the copy. The plugin checks the requesting site before authenticating a key.
- What still works: switching between HTTP and HTTPS, or between the
wwwand non-wwwversion of the same domain, does not affect existing keys — these count as the same site. - Genuine domain move: if you permanently move a site to a new domain, the Connections page marks every key issued before the move as Issued on another site.
- Re-bind: for each key you want to keep working on the new domain, click Re-bind next to it to assign that key to the current site so it authenticates again. Revoke any keys you don't intend to keep instead of re-binding them.
Site-Wide Guardrails
Beyond per-token permissions, Easy MCP AI > Settings provides global controls that apply to every token and OAuth connection:
- Disabled Tools: globally switch off sensitive tools, such as the delete tools or user- and site-management tools. Disabled tools return an error when called, regardless of token permissions. On a fresh install, the account and site-control tools (creating or editing users, changing site settings, editing templates and global styles) are disabled by default.
- Whitelist Tools: restrict the entire MCP server to tools matching glob patterns (for example
wp_get_*, wp_list_*for a fully read-only site). - Rate Limit: the maximum number of tool calls per token per minute.
- IP Whitelist: limit MCP access to specific IP addresses or CIDR ranges.
- Force Draft on Create: every post or page the AI creates is saved as a draft, no matter what status it requests.
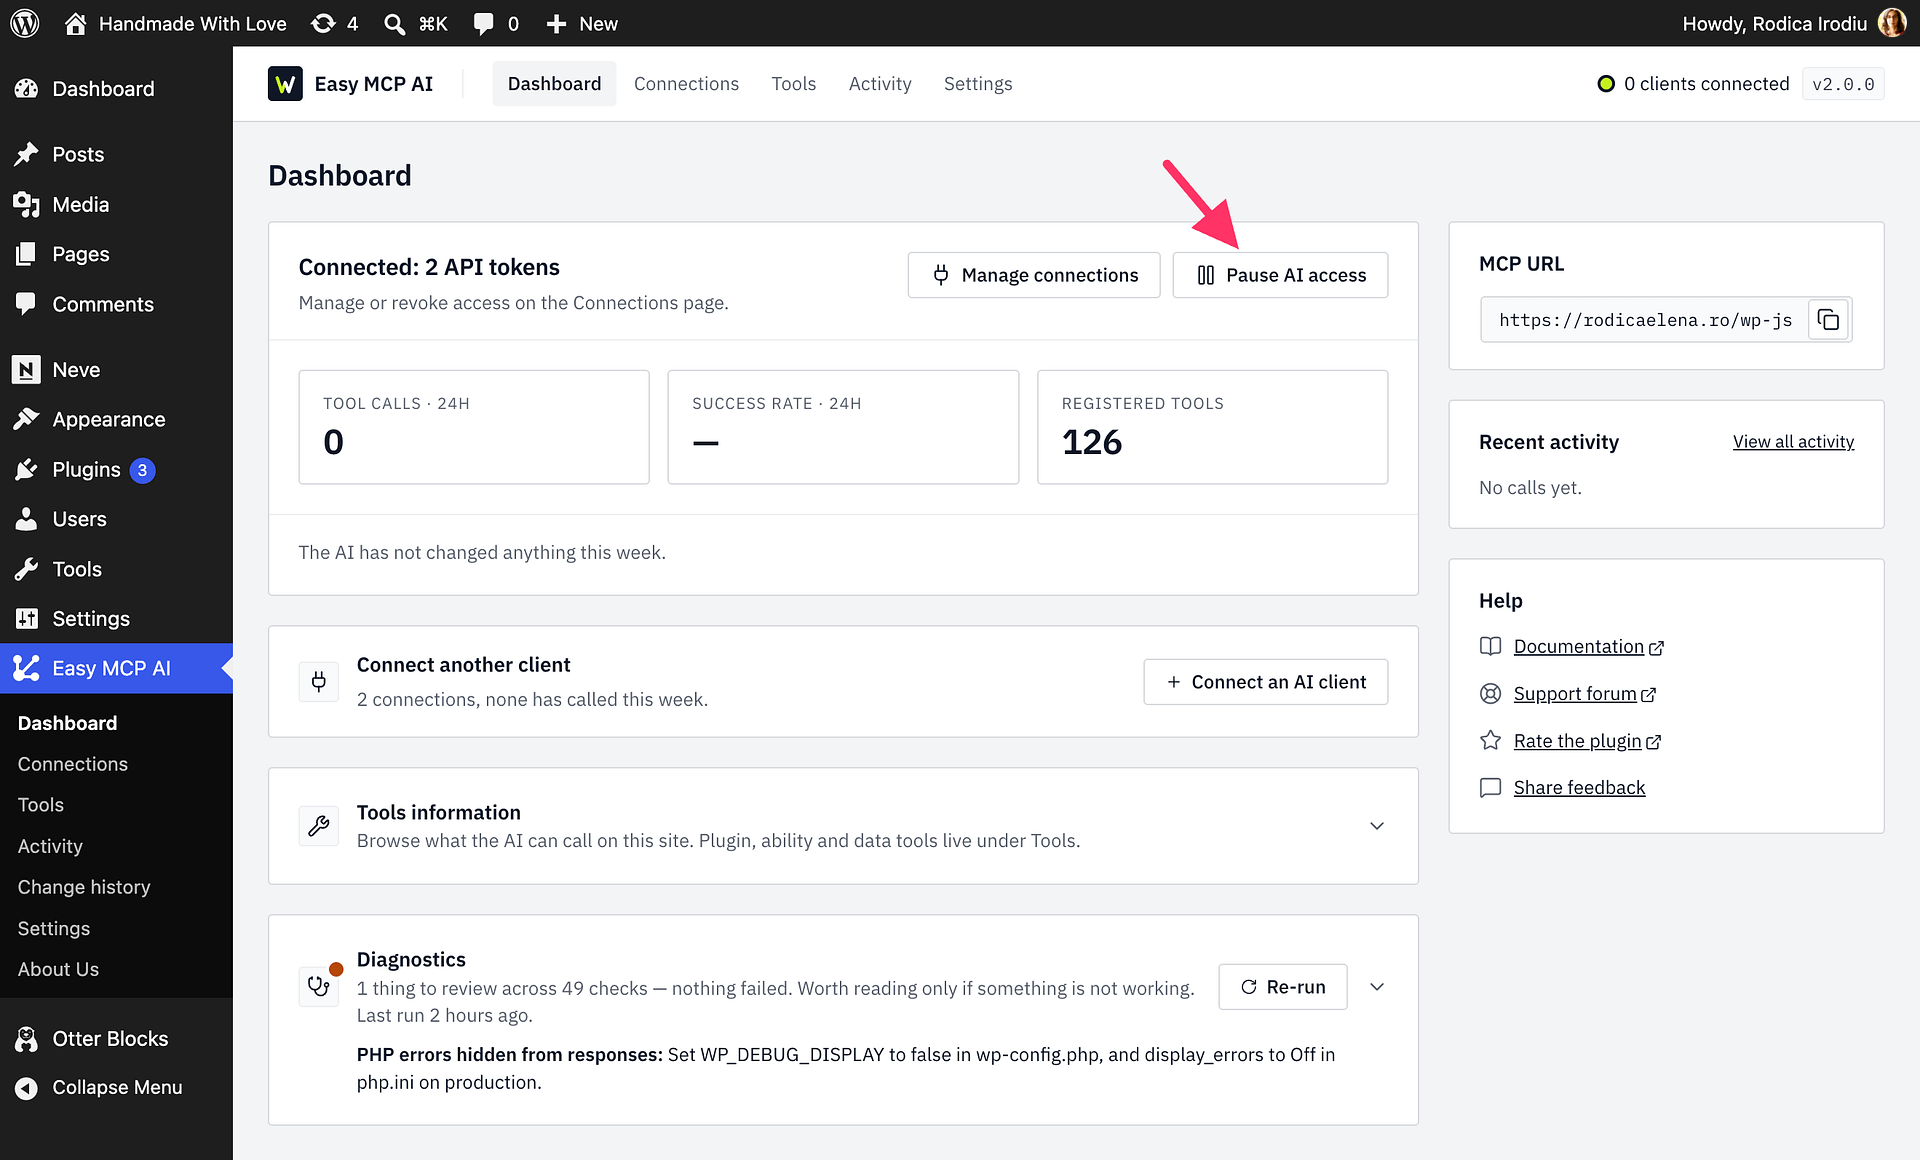
In Easy MCP AI > Dashboard there is a button to Pause AI access.
Pause AI access: temporarily makes the tools/list response empty and refuses every tool call while keeping API tokens and OAuth connections saved. Calls made while access is paused are refused and logged. Resume access from the same control when you are ready.
Auditing What Your Tokens Do
Every tool call is recorded in Easy MCP AI > Activity (when audit logging is enabled in Settings), so you can review exactly what each token has done and when. For a full walkthrough of the Audit Log, see Using the Easy MCP AI Audit Log. Change History additionally stores before/after snapshots of every write performed via MCP. Both logs are pruned automatically after the retention period you configure.
Security
If you identify a potential security vulnerability in this plugin, please disclose it responsibly. Follow the protocols on the Themeisle Security Page.